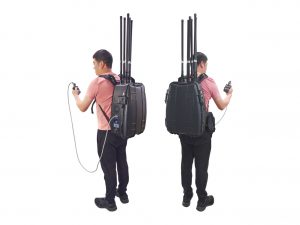
The rapid expansion of low-Earth-orbit satellite constellations has changed how militaries plan for satellite communications. For defense clients, the question is no longer whether to address Starlink and similar services, but how to procure configurable countermeasures that fit legal, operational, and platform constraints. This article examines Starlink jammer customization options for military clients from a market and procurement perspective. It does not provide technical instructions or operational parameters.
Why Customization Is Now a Procurement Requirement
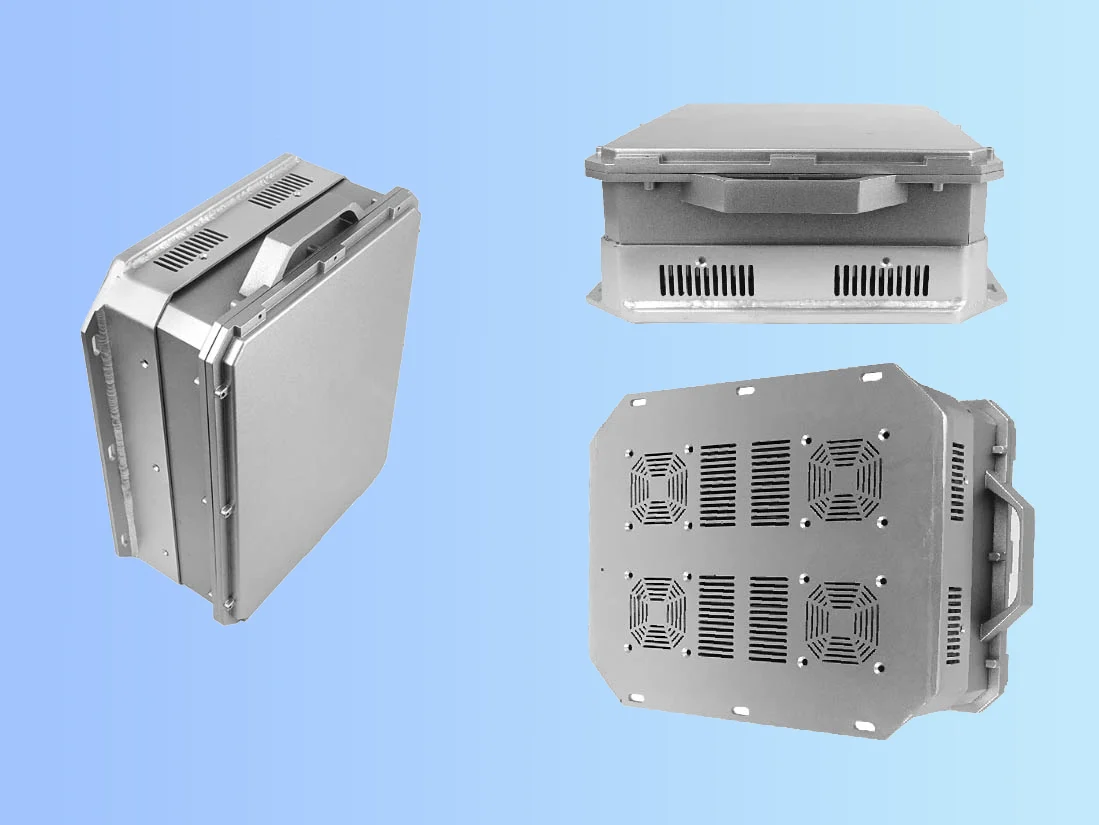
Militaries rarely buy standalone jammers. They buy effects that must integrate with electronic warfare, command-and-control, intelligence, and platform systems. Starlink’s global footprint and evolving network behavior create demand for solutions that can be updated, governed, and sustained over time. Vendors have responded with modular architectures, open interfaces, ruggedized hardware, and lifecycle support packages.
The Main Customization Layers
| Customization Layer | Typical Military Requirement | Programmatic Value |
|---|---|---|
| Platform fit | SWaP-constrained vehicle, naval, airborne, dismounted, or fixed-site variants; ruggedization; EMI/EMC | Deploys without redesigning the host platform |
| Command and control | Open API, C2/EW integration, operator interface, remote updates, role-based access | Fits existing battle-management workflows |
| Spectrum policy management | Country-specific rules, mission geofencing, dynamic restrictions, audit logs | Supports legal review and sovereign control |
| Power and thermal | Duty-cycle profiles, cooling, battery or generator options, redundancy | Improves reliability in contested environments |
| Signature management | Emissions discipline, remote operation, reduced detectable footprint | Enhances survivability and operational security |
| Sustainment | Training, spares, field repair, software maintenance, documentation | Maintains availability over multi-year programs |
| Compliance and export | Export licenses, end-user controls, technology-transfer limits, audit trails | Enables allied sales and lawful deployment |
Integration Priorities for Defense Buyers
Military clients should prioritize open architecture over closed black boxes. A customized system must connect to existing sensors, effectors, and command nodes without forcing a new proprietary ecosystem. Software-defined policy controls are also increasingly important because they allow operators to adjust behavior under changing legal and mission authorities.
Other integration priorities include cybersecurity hardening, operator training, and logistics planning. A system that performs well in a vendor demonstration but cannot be repaired, updated, or audited in the field creates long-term risk.
Testing, Validation, and Assurance
Customization claims should be verified through structured testing. Military programs typically require controlled range trials, spectrum-authority coordination, interference risk assessments, environmental qualification, and C2 integration checks. Independent verification and red-team review can help identify unintended effects and fail-safe gaps.
Documentation matters as much as test results. Buyers should request test reports, compliance matrices, update procedures, and clear statements of operational limitations.
Evaluation Scorecard
| Evaluation Area | Strong Signal | Warning Sign |
|---|---|---|
| Architecture | Open interfaces, documented APIs, modular design | Proprietary closed stack |
| Compliance | Export matrix, end-user controls, legal support | Vague “global” approval claims |
| Testing | Customer-specific trials, modeling, range support | Vendor lab demos only |
| Sustainment | In-country support, training, spares | No local repair or update path |
| Roadmap | Software updates tied to threat evolution | Static hardware-only roadmap |
Legal, Export, and Spectrum Realities
Jamming is tightly regulated. In many jurisdictions, only state actors operating under specific authorizations may conduct it. Military buyers need legal review, spectrum coordination, and clear rules of engagement before fielding any capability. Export controls, end-user certificates, and technology-transfer restrictions may also apply. This article is not legal advice.
What Vendors Should Demonstrate
Vendors targeting military clients should demonstrate sovereign control, compliance by design, interoperability, lifecycle cost transparency, training capacity, and supply-chain security. They should also show a realistic understanding of how defense procurement works, including budgeting cycles, certification requirements, and coalition interoperability needs.
Market Outlook
Demand for counter-LEO SATCOM capabilities is likely to grow as military dependence on commercial satellite services increases. Customization will shift further toward software-defined policy engines, C2 integration, modular hardware, and export-friendly configurations. The strongest vendors will be those that co-develop with defense clients and document compliance at every stage.
Conclusion
Starlink jammer customization for military clients is best understood as a capability integration challenge, not a simple hardware purchase. Buyers should evaluate architecture, compliance, testing, sustainment, and legal authority together. Programs that align operational need with long-term support and lawful deployment will be the most durable.